About CreepyLink
The story behind the internet's most suspiciously-looking URL generator.
What We Do
CreepyLink transforms ordinary web links into theatrically suspicious-looking URLs for harmless entertainment, seasonal surprises, Rickrolls, and authorized cybersecurity awareness training. Our tool gives normal links an alarming cosmetic appearance—featuring parody warning keywords, dramatic parameter strings, and ominous-looking path names—while ensuring the underlying destination remains completely transparent and safe.
Every link generated through CreepyLink leads to an intermediate preview gateway. Before anyone is forwarded to the final URL, they are presented with a clear 5-second review countdown, the exact destination domain, safety reminders, and an explicit manual confirmation button. This ensures that no visitor is ever redirected without their conscious, informed consent.
Our Mission & Cybersecurity Awareness
In an era where cyber threats, phishing scams, and deceptive links are widespread, digital literacy and link inspection have become essential survival skills. Most people are taught to fear links through dry security presentations that are quickly forgotten. CreepyLink was built on a different premise: interactive, humorous, and memorable experiences are far more effective at teaching people to pause and verify before clicking.
By creating links that look alarming on the surface but strictly adhere to ethical safety standards, CreepyLink serves as a practical demonstration tool. Educators, IT security teams, and friends use our platform to show how easily URL appearances can be manipulated, encouraging internet users to develop healthy skepticism and always inspect domain destinations.
Core Safety & Ethical Framework
CreepyLink operates under a strict, non-negotiable safety framework designed to protect users, recipients, and the broader web ecosystem:
- Zero Credential Collection: CreepyLink never creates fake login forms, prompts visitors for passwords, requests multi-factor authentication codes, or attempts to harvest private account credentials.
- No Malware or Forced Downloads: The platform does not host executable files, trigger automated downloads, install browser extensions, or modify browser settings.
- Transparent Interstitial Preview: Every link displays the complete, unmasked destination URL and root domain before allowing the user to proceed.
- Automatic 24-Hour Expiration: All short code mappings automatically expire and are permanently purged from our database within 24 hours of creation, preventing abandoned links from persisting indefinitely.
- No Creator Tracking Dashboards: We do not provide link creators with analytics dashboards, click maps, IP logs, or visitor telemetry.
Official Domain & Similarly Named Sites
The CreepyLink tool covered by this site is served exclusively from creepylink.online. We do not operate, represent, or share data with lookalike domains such as creepylink.com, creepylink.org, or any other similarly named address. A similar name on its own is not evidence of a relationship.
Redirect mappings, user input, and product claims are never shared with those domains. If you encounter a CreepyLink reference on another domain, evaluate that site on its own terms — the policies, safety notes, and redirect behaviour described here apply only to the service on creepylink.online. One exception worth naming: generated links are displayed on a handful of redirect hostnames such as account.croppng.online or account.ballorbit.online. Those are registered and operated by the same operator as creepylink.online, they exist purely to carry the odd-looking link, and they are listed in the privacy policy.
How to check whether a CreepyLink page belongs to this service:
- The page URL uses the creepylink.online domain over HTTPS.
- The product flow is: paste a destination URL, generate a temporary redirect, then review the full destination on a preview page before continuing.
- No page asks for passwords, payment details, account tokens, one-time codes, or file downloads.
Third-party directories, review pages, and listing summaries (for example ProductFame-style entries) are external context only. They are not ownership statements, partnerships, endorsements, or a source of official policy. Use them for discovery, then verify the domain and the product behaviour directly on creepylink.online.
We apply a zero-tolerance policy to abusive usage: adult-content destinations and links pointing back at this service are rejected automatically. CreepyLink does not host malware or create phishing pages, and a link reported for phishing, harassment, fraud, or illegal content is reviewed and may be disabled. To report a link, contact abuse@creepylink.online.
Who Runs CreepyLink
CreepyLink is built and operated by an independent developer — not a company, not an agency, and not a marketing team. There is no sales department behind it: the same person writes the code, runs the redirect infrastructure, answers the abuse inbox, and updates these pages.
The operator publishes under the name Tnagjei — the same handle used for this project's source repository and hosting account. No company or agency sits behind the service; it is a personal project run by one person.
Because it is a one-person operation, support is best-effort rather than around the clock. Abuse reports come first and are reviewed before anything else; feature requests and general questions are answered as time allows. The fastest way to reach the operator is the contact page — the abuse, privacy, and legal addresses all reach the same person.
Operating costs and the absence of tracking products are deliberate: the service is funded by on-site advertising on the content pages, and the data it keeps is limited to what the redirect actually needs. That is stated plainly in the privacy policy rather than buried in a terms page.
Educational Value & Phishing Prevention Insights
Research in behavioral cybersecurity consistently highlights that real-world exposure to simulated social engineering vectors dramatically improves an individual's ability to identify actual threats. When users encounter a CreepyLink demonstration, they experience firsthand the psychological trigger of curiosity versus caution.
By teaching people to look beyond URL cosmetic appearance and actively check domain roots, certificates, and destination parameters, CreepyLink contributes to a safer, more vigilant digital community. We encourage trainers and educators to incorporate our tool into ethical security workshops and digital hygiene curricula.
What Actually Happens, Verified on the Live Service
The screenshot below is a real capture taken from the live service on 21 September 2026, not a mock-up. It shows the intermediate preview that every generated link passes through: the exact destination domain, the full destination URL, and an explicit confirmation button that the visitor must press before anything else happens.
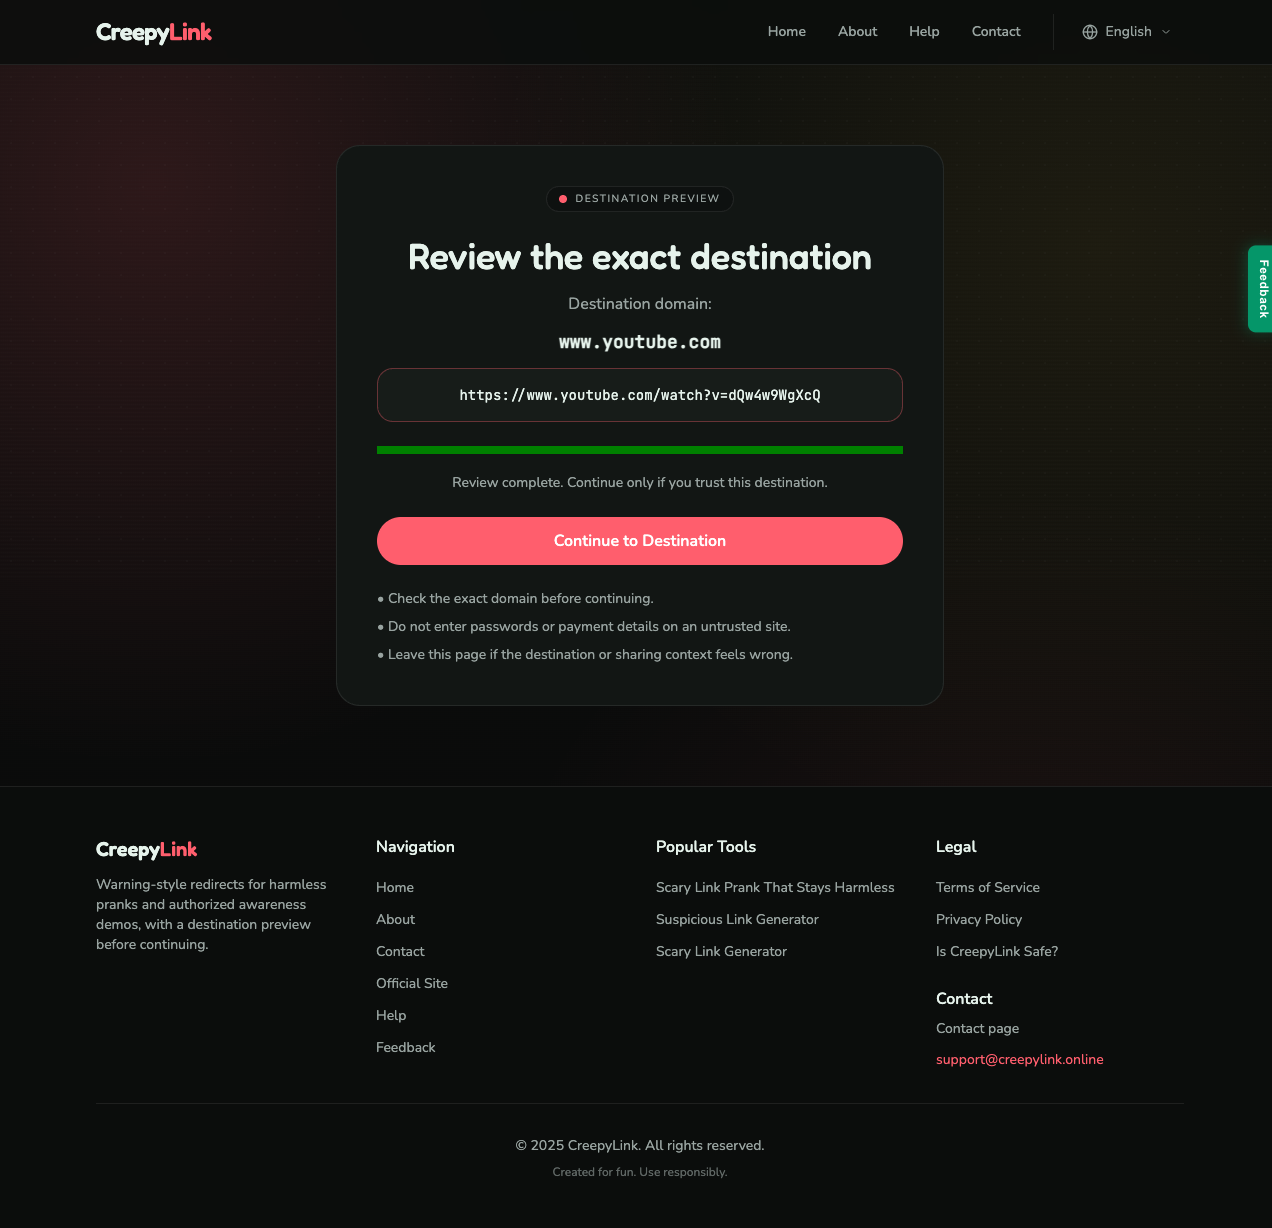
www.youtube.com shown before the visitor can continue.End-to-end behaviour, recorded against the live service on 21 September 2026:
| Step | Request | Observed result |
|---|---|---|
| Create | POST /api/create | 200, temporary code returned |
| Resolve | GET /api/get-url | 200, the exact destination we submitted |
| Legacy path | GET /r/<code> | 302 to the preview page, never straight to the destination |
| Preview | GET /link-preview | 200, review countdown and destination shown |
| Expired code | GET /r/zzzzzz | 302 to the link-error page |
| Unsafe scheme | javascript: target | 400, rejected |
| Malformed URL | non-URL text | 400, rejected |
| Wrong method | GET /api/create | 405, rejected |
What the service is actually used for, measured on 21 September 2026:
- 421 temporary mappings were live inside the 24-hour expiry window at the moment of measurement.
- They pointed at 161 distinct destination hosts.
- About 50% of them were YouTube-family links — the ordinary “send a friend a spooky video link” use case this tool was built for.
- Mappings expire automatically and are purged within 24 hours, so no abandoned link persists.
⚠️ Disclaimer: CreepyLink is for entertainment purposes only. Please don't use it for actual malicious activities. That would be very un-creepy of you.